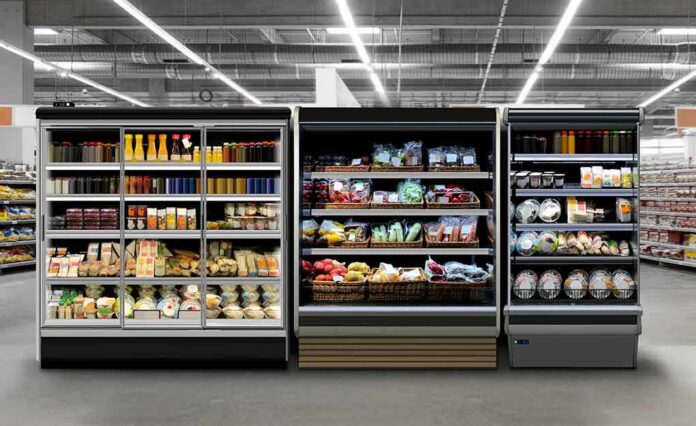
Europe’s food cold chain was jolted after cyberattacks overheated supermarket freezers across at least nine countries, pushing Italy into emergency security talks.
Story Snapshot
- Italy convened ministers and intelligence chiefs after cross-border freezer hacks hit European supermarkets.
- European Union officials warned the incidents looked like a deliberate effort to disrupt food supplies.
- Retailers in multiple nations reported spoiled goods and store closures as systems overheated.
- Security agencies urged stronger protection for operational technology that runs physical systems.
Italian Emergency Talks Treat Freezer Hacks as Security Threat
Italy’s government held emergency talks with ministers, intelligence leaders, and its national cybersecurity authorities after attacks on supermarket refrigeration systems across Europe. Reports cited incidents in at least nine to eleven countries, with freezers pushed to unsafe temperatures and stores discarding food. No group claimed responsibility. After the meeting, the prime minister’s office said the situation did not warrant public alarm, while officials continued to track risks to food logistics and store operations.
Italian officials framed the issue as national security because food refrigeration is a vital service. Attacks on operational systems can quickly create waste, cost, and public concern. Authorities moved to coordinate with European partners and industry to restore normal cooling and prevent repeat events. The incidents followed an earlier disruption in French supermarkets in October, which forced stores to throw away stock after remote tampering of cooling units. That earlier shock showed how fast digital tools can cause real-world losses.
Cross-Border Pattern Points to Critical Infrastructure Exposure
Media and official briefings described a spread of affected locations, from Belgium and Sweden to Italy and Portugal, with multiple retailers reporting abnormal freezer temperatures and spoilage. In Sweden, local stores said systems were set to extreme heat, forcing closures and product disposal. Such common effects across borders suggest attackers targeted similar control systems or service providers, rather than random equipment failures. European Union officials warned the events were not isolated, signaling concern over a wider campaign.
This pattern highlights the risk inside operational technology, the digital controls that run physical processes like cooling and heating. The Cybersecurity and Infrastructure Security Agency says food and agriculture depend on these systems, and intrusions can trigger physical damage or downtime, not just data theft. The European Union Agency for Cybersecurity has also warned that supply chain attacks are growing more complex, often moving through shared vendors or software used by many clients.
Food Supply Stakes: From Spoilage to Public Trust
When freezers fail, meat, dairy, and produce can spoil in hours. Stores then face lost sales, higher costs, and angry customers. Shoppers see empty cases and worry about safety. In October, hundreds of French supermarkets reportedly lost cooling and tossed tons of food after remote tampering, underscoring how attacks can turn a store’s backbone into a liability. The latest wave across several countries revived those fears and showed how quickly food waste and price pressure can rise when core systems go down.
European Union statements that called the events a deliberate attempt to disrupt food supply raised the stakes for governments and retailers. Even when leaders tell the public to stay calm, people judge what they see at the counter. If outages repeat, confidence can erode. That is why Italy’s rapid coordination with intelligence and cybersecurity teams aimed to both fix operations and signal control. Clear updates and visible repairs help maintain trust while investigators track the source.
What Authorities and Retailers Can Do Now
Security agencies advise basic steps that pay off fast: change default passwords, segment networks, and keep remote access off unless needed. The Cybersecurity and Infrastructure Security Agency guidance for industrial systems stresses strong access control, alerting on unusual changes, and tested backups so stores can restore settings quickly after an attack. European cybersecurity reports urge vendors and retailers to audit shared software and service providers, since many modern attacks ride the supply chain.
Update on the supermarket freezer attacks:
• European Commission: the attacks are "not isolated." It held two coordination meetings Tuesday morning, and its spokesperson said: "I would be extremely careful when it comes to attributions."
• Portugal: 7 Intermarché stores linked…— OMBI.MrPresentable (@CouncilShiba) November 3, 2026
Retailers can also practice “freeze-safe” fail modes. That means designing systems so they default to safe temperatures if they lose contact with central controls. Regular drills with staff, clear temperature logs, and manual override training help teams catch and fix issues fast. Governments can support information sharing between chains and countries, since attackers often reuse tools across borders. The faster experts compare notes, the sooner they can close the same door in many places at once.
Sources:
insiderpaper.com, citizen.co.za, nampa.org, thelocal.com, enisa.europa.eu, cisa.gov